
DevSecOps & Code Security
DevSecOps, SAST, application security, and secure coding practices.
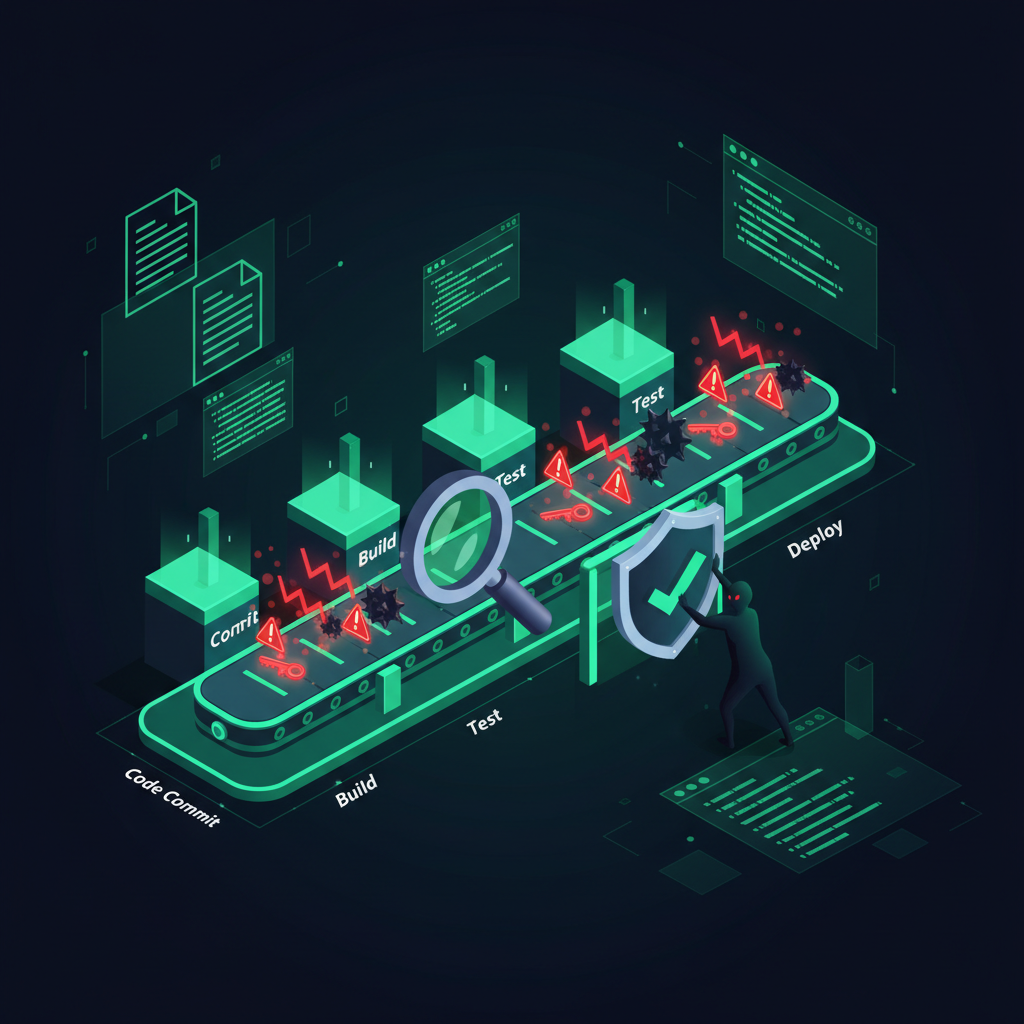
CI/CD Security: Pipeline Hardening, Tools & OWASP Top 10 Risks (2026 Guide)
Why CI/CD Pipelines Became the Attacker's Favorite Target. The SolarWinds breach didn't start with a phishing email or a misconfigured S3 bucket. It…
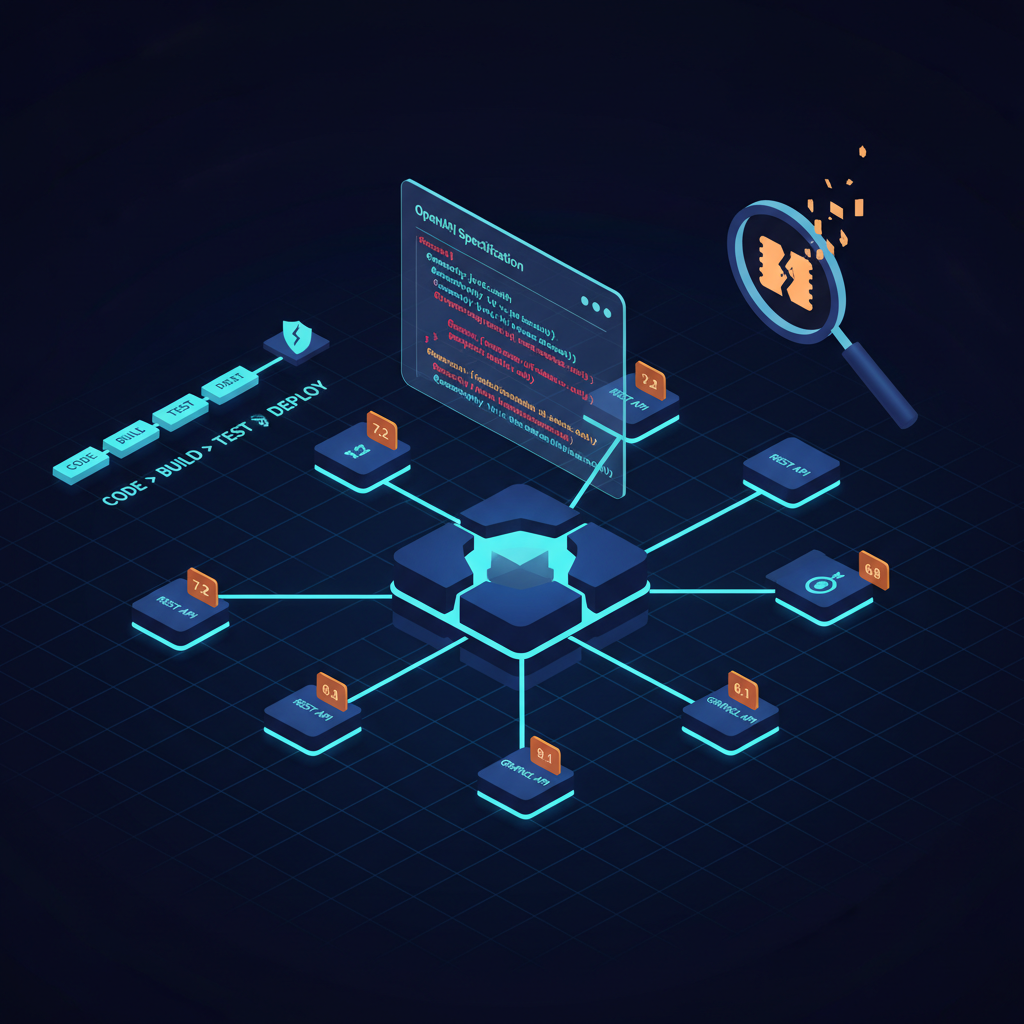
Best API Security Tools & Testing Guide for 2026
APIs Are the New Attack Surface — and Most Teams Are Behind. Salt Security's 2026 State of API Security report found that 94% of organizations…
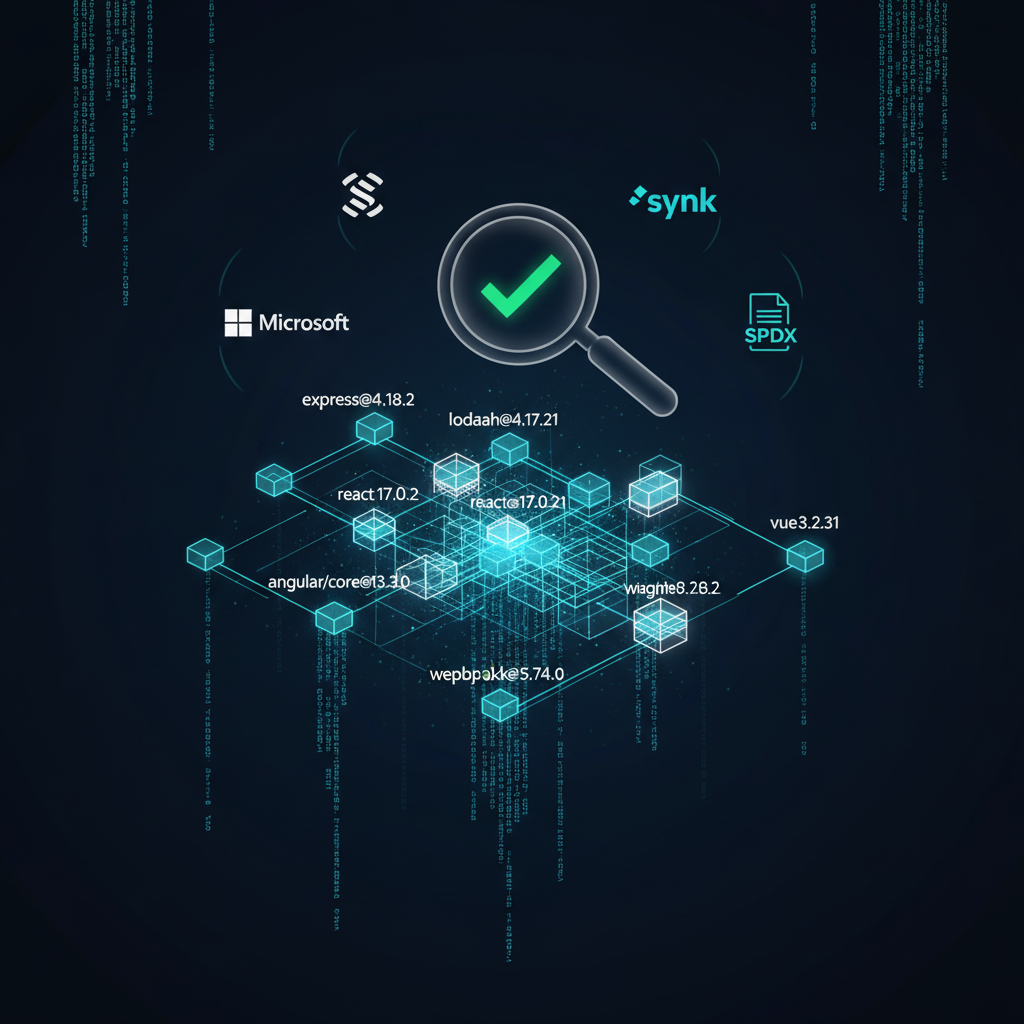
SBOM Generation: Tools, Formats, and Real-World Examples for 2026
Why SBOM Generation Became Non-Negotiable in 2026. The Log4Shell aftermath cost enterprises an estimated $100 million in emergency remediation.…
CI/CD Security: Pipeline Best Practices, Tools & OWASP Risks (2026 Guide)
Why Your CI/CD Pipeline Is Now the Primary Attack Surface. SolarWinds. Codecov. 3CX. The common thread isn't a zero-day exploit or a sophisticated…
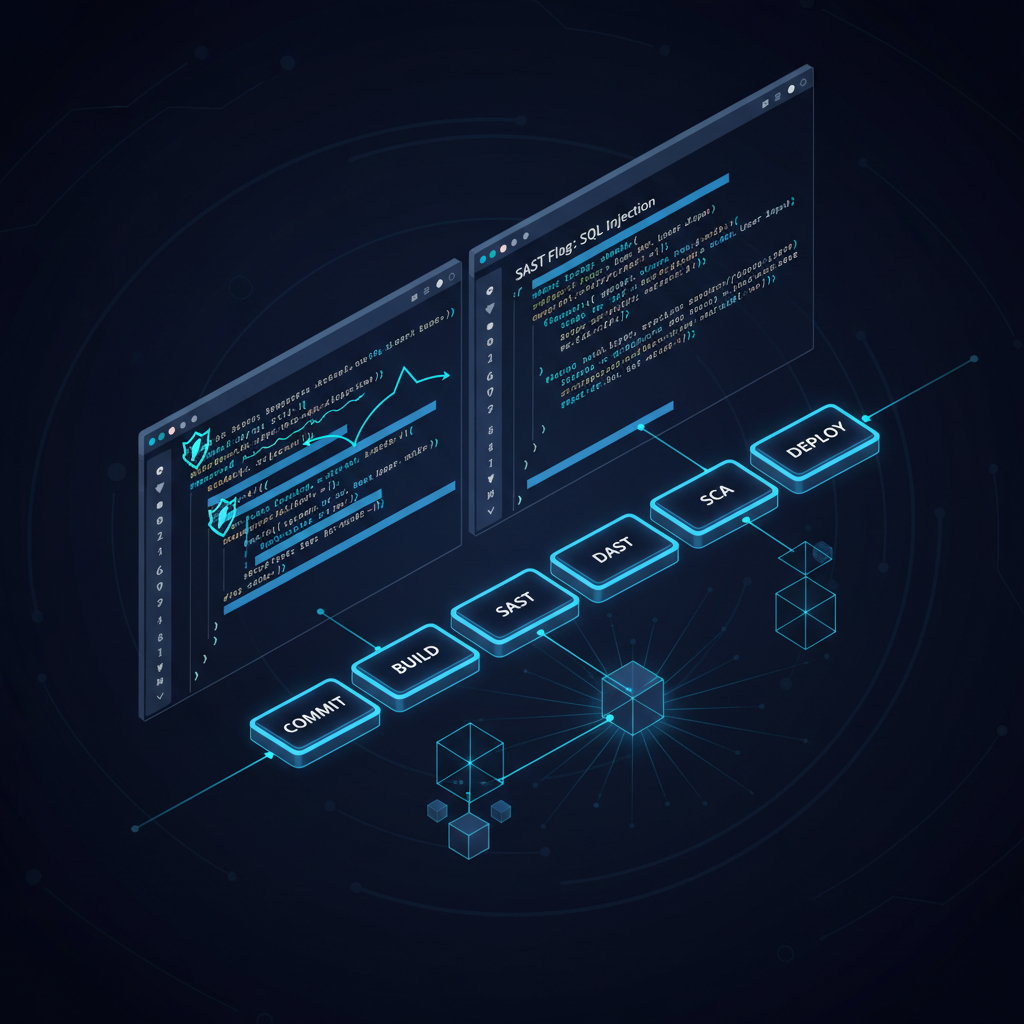
SAST Tools in 2026: How to Pick the Right One (and When to Use DAST or SCA Instead)
Why SAST Tools Are Non-Negotiable in 2026. Veracode's 2026 State of Software Security report found that 76% of applications contain at least one…
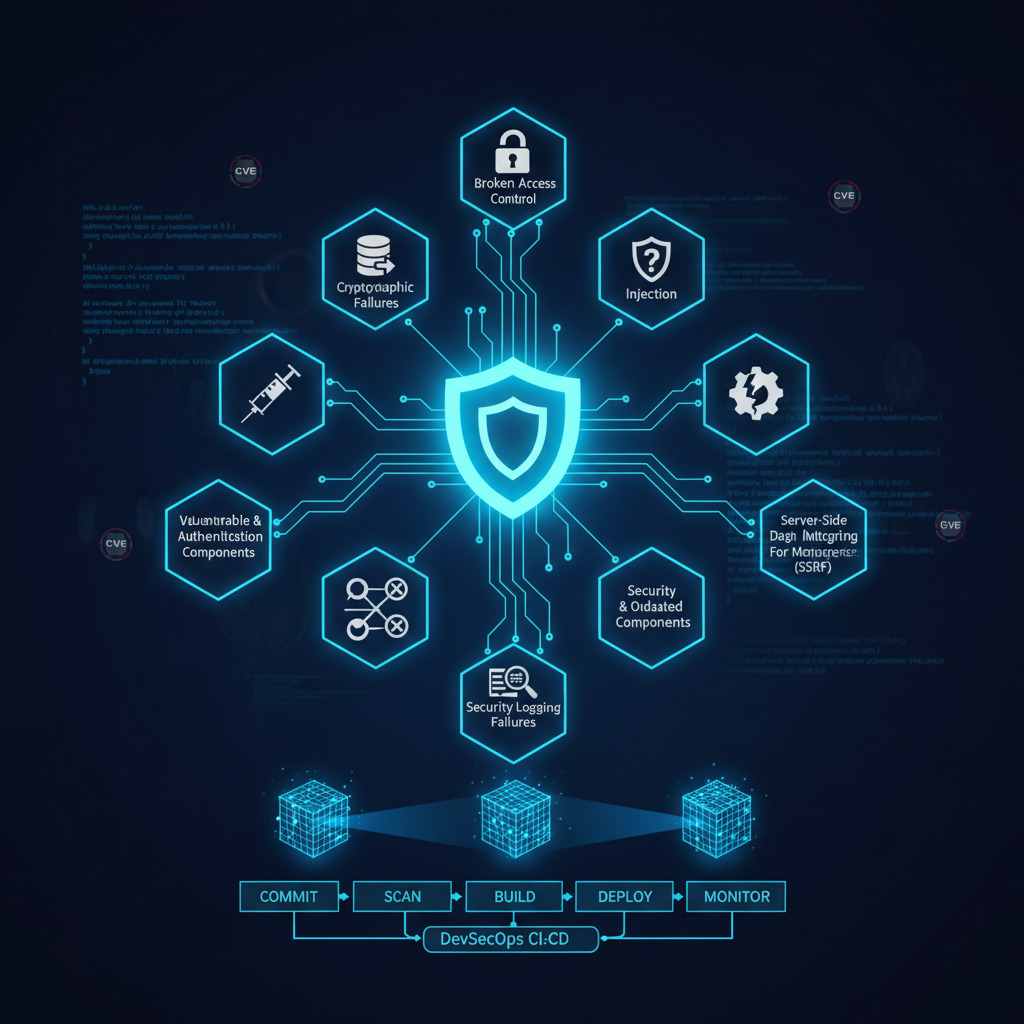
OWASP Top 10 in 2026: What Every DevSecOps Engineer Needs to Know
OWASP Top 10: Still the Most Cited List in Application Security. Roughly 84% of software breaches exploit vulnerabilities at the application layer,…
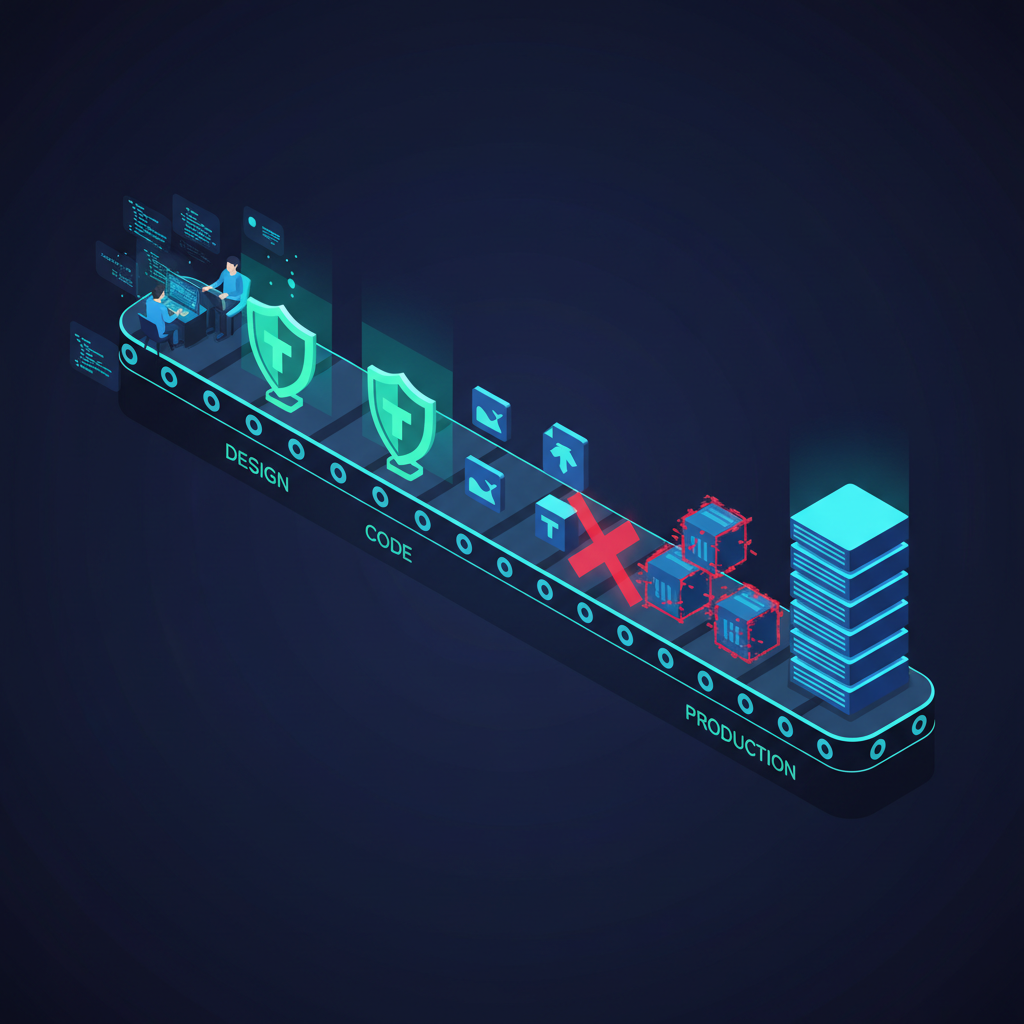
Shift Left Security: Strategy, Best Practices & DevSecOps Integration
The Cost of Finding Bugs Late Is Astronomical. IBM's 2026 Cost of a Data Breach report puts the average breach price at $4.88 million. But here's the…
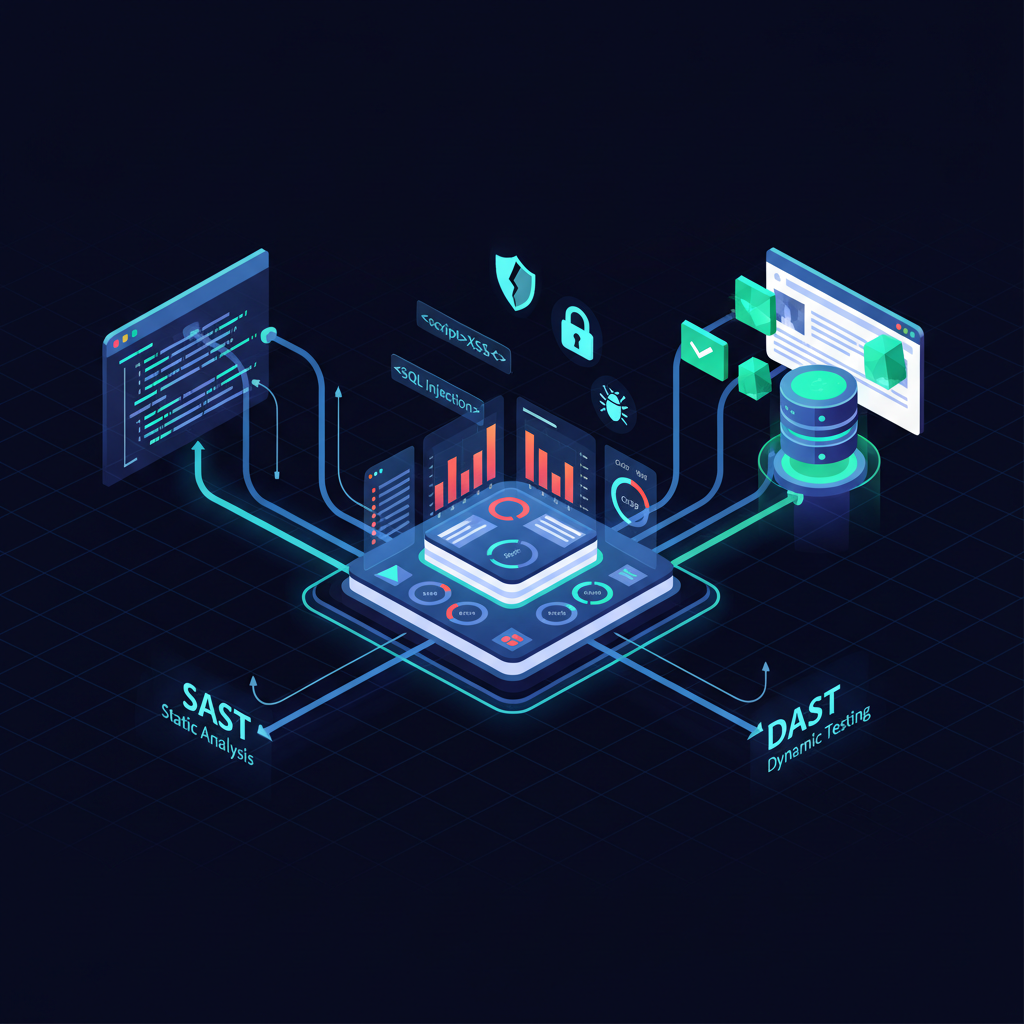
DAST and SAST Tools: The Complete 2026 Guide to Application Security Testing
Roughly 74% of all data breaches traced back to application-layer vulnerabilities in 2026, according to Verizon's DBIR. Not infrastructure…
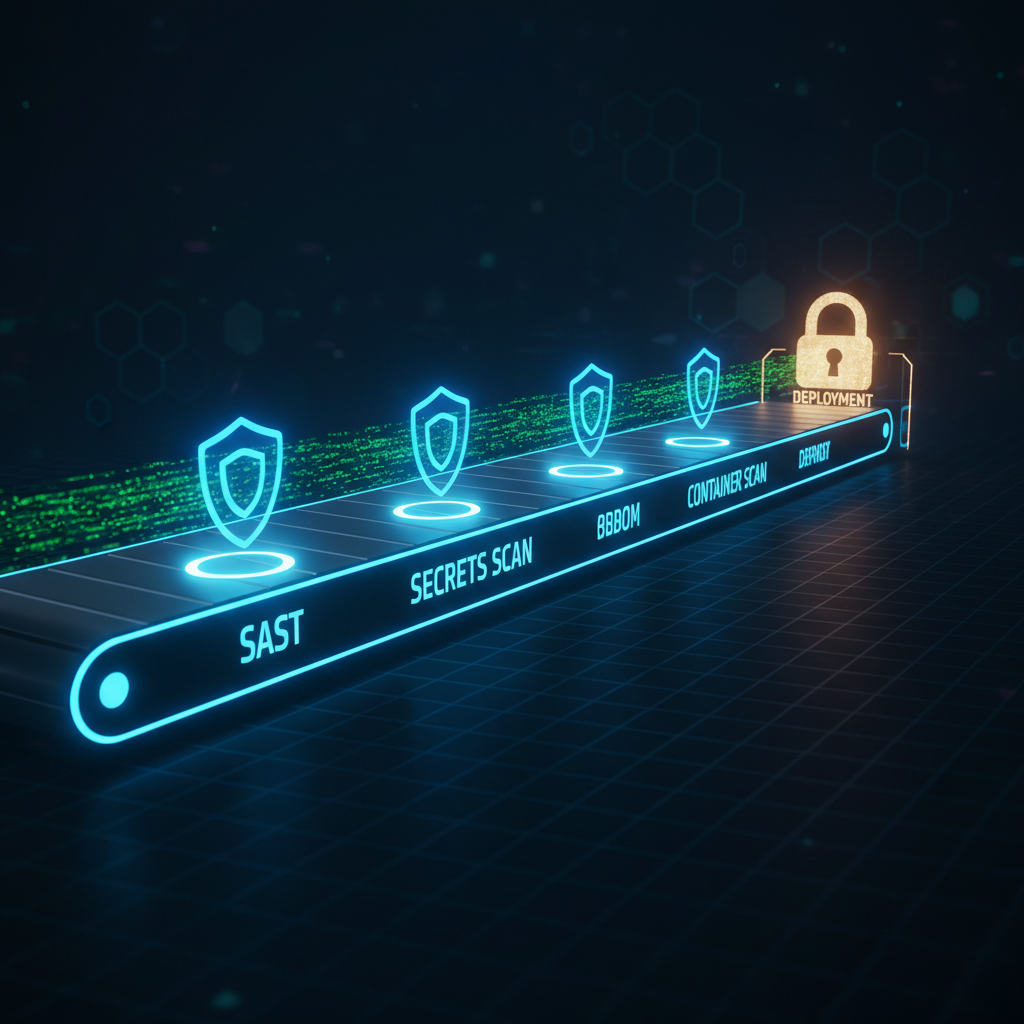
Building a Hardened DevSecOps Pipeline in 2026: The Complete Engineering Guide
Why Most CI/CD Pipelines Are Still Security Disasters Waiting to Happen. Sixty-one percent of organizations experienced a software supply chain…