
GDPR enforcement fines passed 4.2 billion euros cumulatively by mid-2026. A significant slice of those penalties traced back to the same root failure: organisations could not properly handle data subject rights requests. Not ignoring them outright. Just fumbling them. Wrong timelines, incomplete responses, no audit trail.
That is the uncomfortable truth. Most organisations have a privacy policy. Far fewer have an operationally sound process for receiving, verifying, fulfilling, and documenting subject access requests under GDPR. If your team is still copy-pasting responses from an old template and hoping for the best, this guide is for you.
What Are Data Subject Rights Under GDPR?
GDPR Chapter III (Articles 12 to 23) defines a suite of rights that any individual can exercise against any organisation that processes their personal data. These are not optional features. They are legally enforceable entitlements, and supervisory authorities across the EU and UK actively field complaints when they are violated.
Here is the core set:
- Right of access (Article 15) The right to obtain confirmation of whether personal data is being processed and, if so, a copy of it along with supplementary information.
- Right to rectification (Article 16) The right to correct inaccurate personal data without undue delay.
- Right to erasure (Article 17) The right to have personal data deleted under specific conditions, such as when data is no longer necessary for its original purpose.
- Right to restriction of processing (Article 18) The right to limit how personal data is used while a dispute is resolved.
- Right to data portability (Article 20) The right to receive personal data in a structured, commonly used, machine-readable format and transmit it elsewhere.
- Right to object (Article 21) The right to object to processing based on legitimate interests or direct marketing.
- Rights related to automated decision-making (Article 22) Protections against decisions made solely by algorithms that produce significant effects on the individual.
Each right has its own scope, conditions, and exceptions. Getting them mixed up or applying the wrong standard to a request is a compliance failure in itself.
What Is a Subject Access Request?
A data subject access request, commonly abbreviated as SAR or DSAR, is the formal mechanism through which an individual exercises their Article 15 right. Effectively, they are asking: what personal data do you hold about me, why, where does it come from, and who have you shared it with?
A compliant response to a subject access request must include:
- Confirmation that personal data is or is not being processed
- A copy of that personal data
- The purposes of processing
- The categories of data involved
- Recipients or categories of recipients
- Retention periods or the criteria used to determine them
- The existence of other data subject rights including rectification, erasure, restriction, and objection
- The right to lodge a complaint with a supervisory authority
- The source of data, if not collected directly from the subject
- Details of any automated decision-making including profiling logic
That is a non-trivial response to assemble, especially at scale. Organisations receiving hundreds of SARs per month need automated tooling and clear internal workflows, not ad hoc processes.
The 30-Day Time Limit for GDPR Subject Access Requests
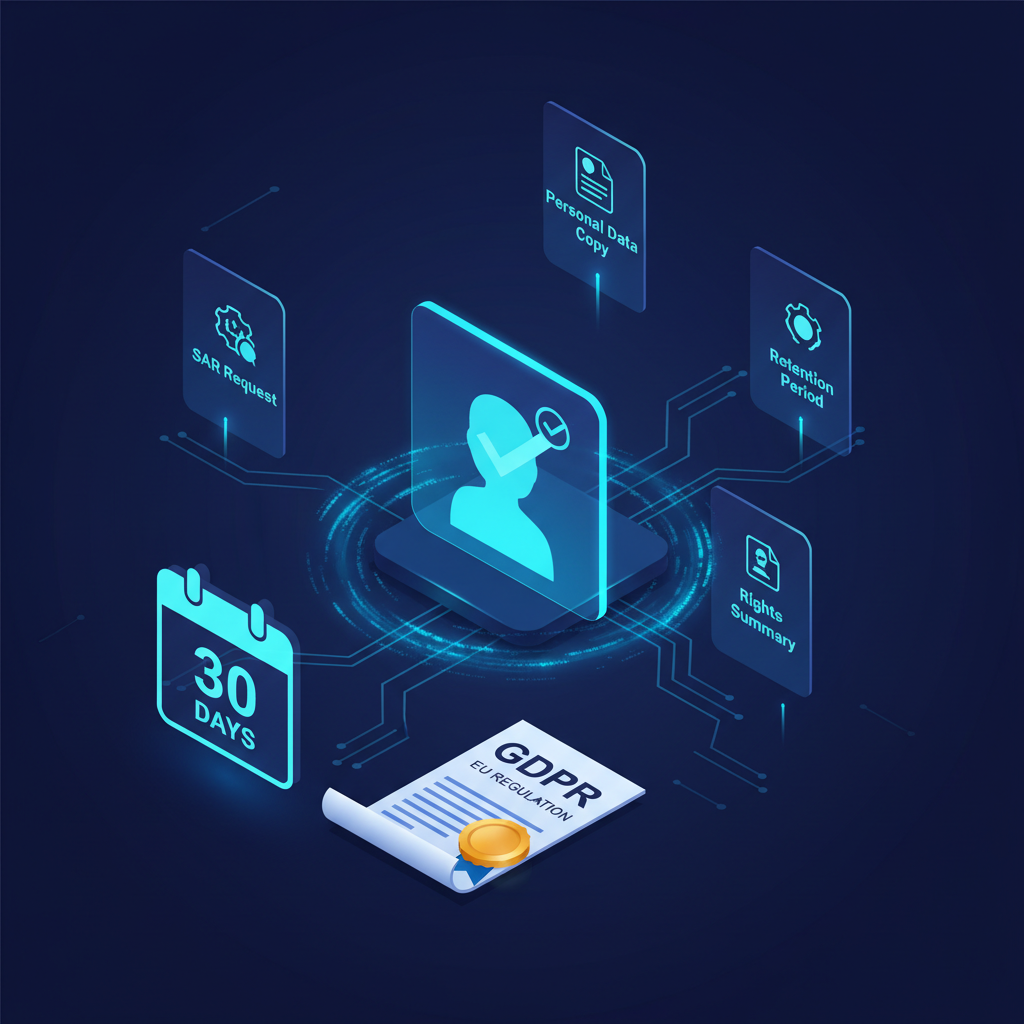
Under Article 12(3) of the GDPR, organisations must respond to a data subject access request without undue delay and in any event within one calendar month of receipt. That is the standard data subject access request time limit. The clock starts ticking from the day the request is received, not the day it is logged internally or the day someone finally reads it.
There is a one-off extension available. If the request is complex or you have received a high volume of requests simultaneously, you can extend the deadline by a further two months. But you must inform the individual within the initial one-month window and explain why you need the extra time. Silence past 30 days is a breach.
What counts as complex? The ICO and EDPB guidance both suggest that complexity relates to the nature of the data or the difficulty of identifying and extracting it, not internal resourcing constraints. Being short-staffed is not a valid reason to invoke the extension.
Data Subject Access Request UK Rules After Brexit
Since the UK left the EU, UK GDPR operates under the retained UK Data Protection Act 2018. The practical rules around subject access requests are almost identical to EU GDPR. The same one-month time limit, the same response requirements, and the same right to extend for complex cases all apply.
The key differences to watch are:
- Supervisory authority: The Information Commissioner's Office is the UK regulator. Complaints go to the ICO, not an EU data protection authority.
- Manifestly unfounded or excessive requests: UK GDPR Article 12(5) allows organisations to charge a reasonable fee or refuse requests that are manifestly unfounded or excessive. The ICO has published guidance on what this means in practice.
- Adequacy status: The UK adequacy decision with the EU remains in place as of 2026. Transfers of personal data between the UK and EU continue under that framework, which is relevant when your SAR response involves data that originated in an EU member state.
If your organisation operates across both jurisdictions, you need to track which legal basis applies to which data subject and route their SAR to the correct response framework.
Building a Compliant SAR Response Process
Theory is one thing. Operationalising data subject rights at scale is where most compliance programmes fall apart. Here is what a mature process looks like.
Step 1: Identity Verification
Before handing over personal data, verify you are responding to the right person. GDPR does not prescribe a specific verification method, but the standard is proportionate assurance. For a customer who submits via an authenticated portal, that is usually sufficient. For email requests, you might ask for additional information, but you cannot demand excessive documentation like certified ID copies for routine requests.
The ICO guidance is pragmatic here. If you have reasonable doubt about identity, ask for clarification. If you have no doubt, proceed. Do not use verification as a stalling tactic, because regulators see through it.
Step 2: Data Discovery and Mapping
You cannot respond to a SAR if you do not know where your data lives. This is the part that exposes weak data governance. Personal data sprawls across CRM systems, marketing platforms, cloud storage, data warehouses, backups, and third-party processors. Without a maintained data inventory, ideally a Record of Processing Activities under Article 30, assembling a SAR response becomes a manual archaeology project.
Tooling matters here. Platforms that give you continuous visibility into your data landscape become essential infrastructure for privacy teams, not just security teams. The kind of real-time cloud asset context available through cloud inventory capabilities is directly applicable to understanding where personal data sits across your estate. If you cannot enumerate what data you hold, you cannot fulfil SARs reliably.
Step 3: Scoping and Redaction
Not all data in a SAR response gets disclosed. Third-party data, meaning information about other individuals embedded in the same records, must be redacted. Trade secrets, legally privileged material, and data subject to specific exemptions such as law enforcement and national security can also be withheld. Document your redaction decisions. If challenged, you need to demonstrate you applied exemptions legitimately, not arbitrarily.
Step 4: Response Assembly and Delivery
GDPR Article 12(1) requires responses in a concise, transparent, intelligible, and easily accessible form using clear and plain language. For a SAR, that means the data subject should actually be able to understand what you have sent them, not receive a 400-page unstructured database dump with no explanation.
Delivery format matters. Where technically feasible, provide data in a machine-readable format alongside a human-readable summary. If the data subject made the request electronically, respond electronically unless they request otherwise.
Step 5: Documentation and Audit Trail
Every step of the SAR process, from receipt and verification through data discovery, redaction decisions, response delivery, and any extension invocations, needs to be logged with timestamps. Regulators investigating complaints will ask for this evidence. Maintaining it also helps you identify process bottlenecks and improve turnaround times.
This documentation discipline connects directly to broader compliance programme management. Teams already running SOC 2 or ISO 27001 programmes have evidence collection habits that translate well to GDPR SAR management.
What to Include in a Data Subject Access Request Template
A good DSAR response template is not a form letter. It is a structured framework that prompts responders to include every required element. Here is the core structure:
- Acknowledgement section: Date of request receipt, identity verification status, expected response date.
- Confirmation of processing: Clear statement of whether the organisation processes the subject's personal data.
- Data copy: The actual data, formatted accessibly, with categories labelled.
- Processing purposes: Why each category of data is processed and the legal basis such as consent, contract, or legitimate interest.
- Retention periods: How long each data category is retained and the criteria for that determination.
- Recipient disclosure: Categories of third parties with whom the data has been shared including processors, sub-processors, and public authorities.
- Rights summary: A brief, readable explanation of their remaining rights covering rectification, erasure, restriction, objection, portability, and complaint.
- Exemptions applied: If anything has been withheld or redacted, a clear explanation of the legal basis for that decision.
Organisations with mature compliance frameworks often integrate SAR templates into their Privacy Information Management System so that responses are version-controlled, approved, and consistently applied across teams.
The Intersection of Data Subject Rights and Security
Here is an angle that often gets missed in purely legal discussions of GDPR. Data subject rights processes create security risks if poorly designed. A SAR response channel that does not properly verify identity is an information disclosure vulnerability. An attacker submitting a SAR on behalf of a target could potentially extract sensitive personal data about that individual if your verification controls are weak.
Similarly, automated portability exports, where systems generate bulk data packages for individual users, are attractive targets. If a portability export endpoint is misconfigured or lacks proper access control, it becomes an exfiltration vector. The security team and the privacy team need to be designing these systems together, not in separate silos.
This is where policy-as-code approaches become genuinely useful. Encoding privacy controls such as access verification requirements, export rate limiting, and logging requirements as machine-enforceable rules rather than word documents that developers may or may not read gives you consistent, auditable enforcement at the system level.
Code-level vulnerabilities in the systems handling personal data are also fair game. Static application security testing during development catches injection flaws, broken access controls, and insecure data exposure patterns before they reach production, directly reducing the risk of a personal data breach that would trigger GDPR Article 33 notification obligations on top of the SAR management overhead.
Manifestly Unfounded and Excessive Requests
Article 12(5) GDPR allows organisations to refuse or charge a fee for requests that are manifestly unfounded or excessive, particularly if repetitive. This is a narrow exception, not a general escape hatch. The burden of demonstrating that a request meets this threshold falls on the organisation, and regulators interpret it strictly.
What does manifestly unfounded look like in practice? A request accompanied by an explicit statement that it is intended to harass or cause disruption. What does not qualify includes requests from disgruntled ex-employees, requests that are inconvenient, or requests that require significant effort to fulfil. Volume alone does not make a request excessive.
If you decide to refuse or charge, document your reasoning meticulously. A challenge before the ICO or a data protection authority where you cannot justify the refusal will go badly.
Enforcement Trends: What Regulators Are Actually Penalising
Looking at enforcement actions through 2025 and into 2026, the pattern is clear. Supervisory authorities are not just pursuing headline-grabbing cases against large technology companies. They are issuing fines against mid-market organisations for predictable, preventable failures:
- Failing to respond within the one-month time limit
- Providing incomplete or unintelligible responses
- Applying manifestly unfounded exemptions without justification
- Using verification procedures that effectively block access through disproportionate identity requirements
- Not having any documented SAR process at all
The EDPB coordinated enforcement action in 2026 focused specifically on data subject rights processes. Several national data protection authorities issued corrective orders and fines to organisations that lacked documented procedures, even where no breach had occurred. Process maturity is itself an enforcement target now.
Connecting Data Subject Rights to Your Broader Privacy Programme
GDPR compliance is not a checklist you complete once. Data subject rights management only works properly when it sits within a coherent privacy programme that includes data mapping, retention management, third-party processor oversight, and incident response.
Your privacy policy is the public-facing document that tells individuals what rights they have and how to exercise them. It needs to accurately reflect your internal processes, not just legally compliant boilerplate. If your policy says respond within 30 days but your internal service level agreement is 45 days, you have an inconsistency that a regulator will notice.
The SECRAILS security and privacy blog covers the full spectrum of compliance topics, from cloud configuration to application security, that intersect with data protection obligations. And for teams building the technical infrastructure that underpins GDPR compliance, the SECRAILS platform provides the cloud visibility, code security, and policy enforcement capabilities that privacy programmes depend on. A SAR response process that exposes a data breach is strictly worse than no process at all, which is why security and privacy engineering need to be designed together from the ground up.